A log entry is not automatically evidence
A timestamped event may lack source identity, synchronized time, configuration context, integrity protection or a clear relationship to the resulting action.
Evidence design starts with the claims that engineers, operators, investigators or authorities may need to examine and the records required to support them.
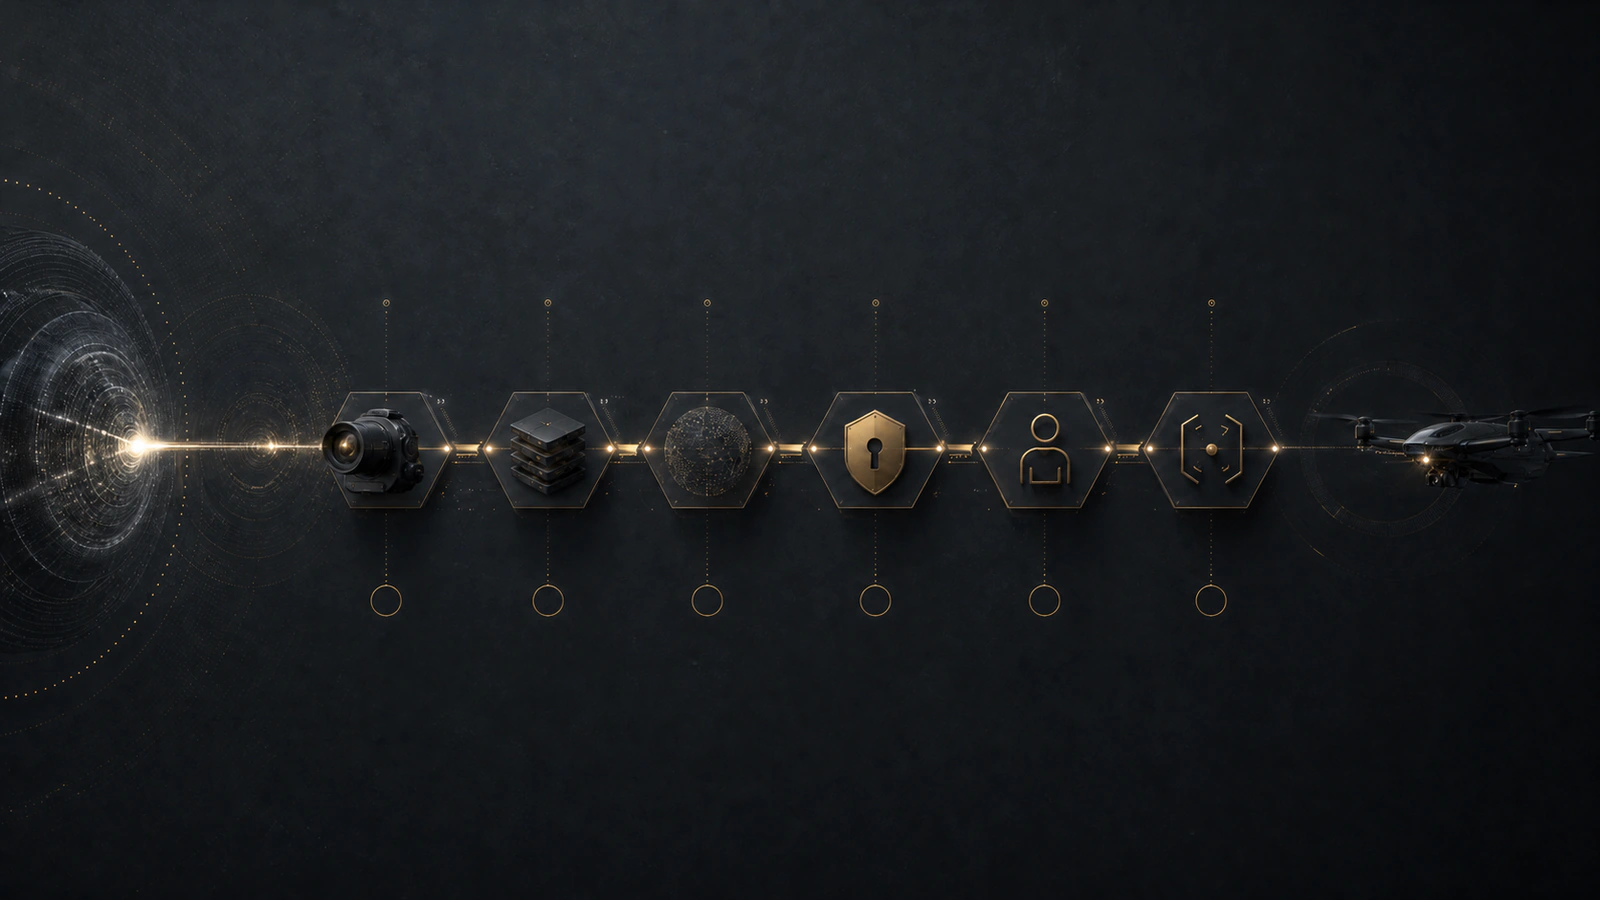
Connect sensor, decision, authority and action
Source and context
Sensor or source identity, time, integrity status, quality, transformations and known limitations.
Decision and execution
Configuration, policy, delegated authority, runtime assessment, selected outcome and resulting action.
Preserve provenance across lifecycle changes
Evidence loses meaning when model, software, data, policy or hardware versions cannot be identified.
Provenance should show which entities and activities produced a result, what changed, who or what authorized the change, and which earlier evidence remains applicable.
Protect integrity without overstating proof
Cryptographic mechanisms can help reveal alteration and bind records to identified sources. They cannot make an incorrect sensor input true or prove that a decision was correct.
Provenance strengthens verification and accountability; it does not replace validation, testing or human judgment.
Support controlled and interoperable use
Evidence architecture must account for classification, privacy, commercial sensitivity, access, retention and selective disclosure.
BIT is designing vendor-independent records for integration with engineering, audit, safety and security workflows. Exact formats remain implementation-specific.
Frequently asked questions
How is provenance different from logging?
Logging records events. Provenance records origin, relationships, agents, transformations and configuration context needed to interpret those events.
Does a complete chain prove the decision was correct?
No. It shows how a decision was produced and whether the record remained intact. Correctness depends on source quality, policy and implementation.
Can sensitive missions protect the evidence?
Yes. Design can include minimization, segmentation, encryption, role-based access, retention limits and selective disclosure.
Can evidence span different vendors?
That is a design objective. Practical interoperability depends on agreed identifiers, schemas, time sources, interfaces and trust anchors.
Sources and technical basis
- W3C PROV-O — The PROV Ontology — Reference inclusion establishes technical context only; it does not claim conformity, approval or certification.
- Regulation (EU) 2024/1689 — Artificial Intelligence Act
- NIST SP 800-218 — Secure Software Development Framework
- NTIA — Minimum Elements for a Software Bill of Materials
- NIST Artificial Intelligence Risk Management Framework
Make critical autonomous actions reconstructable.
Define the evidence claims, provenance model, integrity controls, interfaces and retention requirements for one mission thread.
Review evidence architectureUnclassified · scoped workshops and pilot design